Gain Segregation of Duties (SoD) and Access Reviews in Coupa
As organizations increasingly rely on Coupa for business spend management, ensuring strong Segregation of Duties (SoD) and effective access reviews has become critical. With rising regulatory scrutiny and expanding SaaS environments, risk managers must take proactive steps to identify, assess, and mitigate access-related risks.
What Actions Can Risk Managers Start Taking Now?
To build a strong SoD framework, risk managers should begin by collaborating with:
- Business teams
- Process owners
- Managers and subject matter experts
The goal is to identify key, high-risk, high-level business activities across the organization that are most relevant to SoD.
For example, vendor master data management is widely considered a high-risk Procure-to-Pay (P2P) area across most organizations.
Focus on Critical Systems and Configurations
Risk assessments should start with critical configurations within:
- Accounts Payable
- Procurement systems
- ERP and spend management platforms such as SAP, Coupa, and Oracle
From there, organizations should conduct business process walkthroughs and scope assessments to identify more granular access risks. Begin with the highest-risk areas first, then progressively move to lower-risk processes.
A Comprehensive Audit Solution for Coupa
1Trooper delivers a comprehensive audit and compliance solution designed to automate and simplify SoD and access reviews for Coupa, an all-in-one platform for business spend management.
A key question every organization should ask regularly is:
Who has access to your Coupa data?
Whether driven by regulatory requirements such as Sarbanes-Oxley (SOX) or internal security policies, continuous access visibility is essential.
Integrated Control Management and Continuous Monitoring
With 1Trooper, organizations gain an integrated solution for:
- Access certifications
- Periodic access reviews
- Segregation of duties analysis
- Continuous monitoring and testing
Reporting on who has access to critical Coupa functions helps eliminate unauthorized or orphaned users. By analyzing permissions against a robust SoD ruleset, organizations can clearly identify and address existing risks within Coupa.
Key Features of 1Trooper for Coupa
Access Review and Reporting
- Security access review and SoD analysis down to role, action, and controller level
- Audit report design and scheduling for non-technical users
- Security reports by user, organization, and role/action/controller
- Easy export of reports to Excel for analysis and distribution
- Repeatable automation to ensure continuous compliance
Advanced Segregation of Duties Analysis
- Built-in Coupa-specific SoD ruleset, designed by certified auditors
- Ability to record and report conflict mitigations directly in the application
- Automated controls that reinforce ongoing compliance
- Cross-platform integration to analyze risks across multiple systems on a single dashboard
Why Choose 1Trooper?
As a Software-as-a-Service (SaaS) provider, 1Trooper is committed to delivering solutions that seamlessly empower organizations to take control of their:
- Security
- Compliance
- Risk management initiatives
We help simplify audit processes, strengthen internal controls, and ensure continuous compliance, allowing teams to focus on business growth rather than manual controls.
Strengthen Coupa Security and Compliance with 1TRS
At 1TRS – 1Trooper Risk Services, we enable organizations to confidently manage SoD and access risks in Coupa through automation, visibility, and intelligent reporting.
Ready to Improve SoD and Access Reviews in Coupa?
Discover how 1Trooper can help you achieve continuous compliance and risk visibility.
- #1Trooper
- Coupa Access Reviews
- Coupa Security
- Segregation of Duties (SoD)
- SoD in Coupa
Related articles
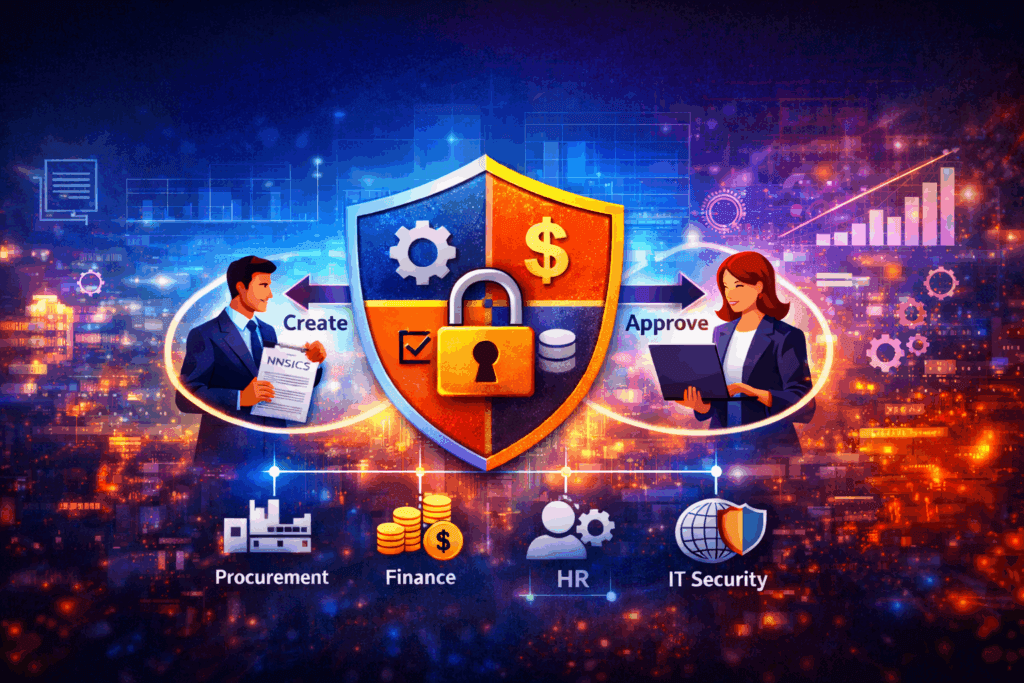
Segregation of Duties: The Most Critical and Complex Control in Modern ERP
In today’s digital-first enterprises, ERP systems sit at the core of business operations, supporting finance, procurement, HR, supply chain, and mission-critical decision-making. While these platforms enable scale and efficiency, they also introduce a significant risk when access is not governed correctly: conflicting or excessive user privileges. This is where Segregation of Duties (SoD) becomes not just important, but essential. Why…
How ERP Role-Based Access Control Aligns Functional Efficiency and Security?
As enterprises scale and digitize operations, ERP environments become increasingly complex, supporting multiple departments, geographies, partners, integrations, and automation. While this complexity enables growth, it also introduces significant access and security risk. The challenge for modern organizations is clear: how do you maintain operational efficiency without compromising security? The answer lies in a well-designed ERP role-based access control (RBAC) tool. Understanding…
Identity Governance for ERP Isn’t Complete Without Segregation of Duties
As enterprises continue to modernize their ERP environments, identity has become the new security perimeter. Users, roles, service accounts, bots, and third-party integrations now access critical ERP functions across finance, HR, procurement, and supply chain operations. While many organizations invest heavily in access controls and role management, identity governance for ERP remains incomplete without one foundational control: Segregation of Duties…