Real-World Governance and Cost-Effectiveness
Introduction
In today’s regulatory environment, organizations across industries—whether corporate, non-profit, or educational—are under mounting pressure to meet compliance requirements. While compliance is critical, the path to achieving it can often be time-consuming, complex, and costly. Worse still, compliance does not always translate into true risk reduction, leaving organizations exposed despite meeting the “check-box” requirements.
This is where real-world governance and cost-effectiveness come into play. To succeed, enterprises must balance compliance obligations with sustainable risk management strategies.
Risk Management vs. Compliance

Compliance and risk management are often treated as interchangeable, but they are not the same. Compliance offers a snapshot of security at a single point in time—similar to a photograph. An organization may “look secure” for an audit, yet still remain highly vulnerable the next day.
Key differences include:
- Compliance ensures adherence to external regulations but may not address ongoing threats.
- Risk Management is a continuous, proactive approach that adapts to evolving security challenges.
In short, an organization can be compliant without truly being secure—and the cost of compliance without proper governance can be devastating.
Governance, Risk, and Compliance (GRC) in Practice
Many businesses view security only as a cost center, overlooking its role in protecting the organization’s reputation, data, and longevity. A well-structured Governance, Risk, and Compliance (GRC) program changes this perspective by aligning security with business objectives.
- Large enterprises may absorb fines and move forward, but smaller organizations risk financial ruin if breaches or penalties occur.
- Real-world governance helps organizations develop mature risk management programs that go beyond check-box compliance.
- Cost-effectiveness is achieved when governance frameworks prevent breaches, reducing long-term expenses and safeguarding business continuity.
Conclusion
Compliance may keep regulators satisfied, but it does not guarantee security. An organization can complete every form, pass every audit, and still face a catastrophic breach. The true value lies in building a risk-aware culture with strong governance practices, ensuring that compliance efforts also enhance real-world security and cost-effectiveness.
1tropper IAM enables enterprises to strengthen governance, manage risk more effectively, and reduce costs—bridging the gap between compliance and true security.
About 1tropper
1tropper is a trusted identity governance platform that blends innovation, security, and cost-effectiveness. Our solutions help enterprises not only meet compliance requirements but also develop stronger governance frameworks to mitigate risks in the real world.Discover how 1tropper can optimize your governance strategy: www.1trooper.com
Related articles
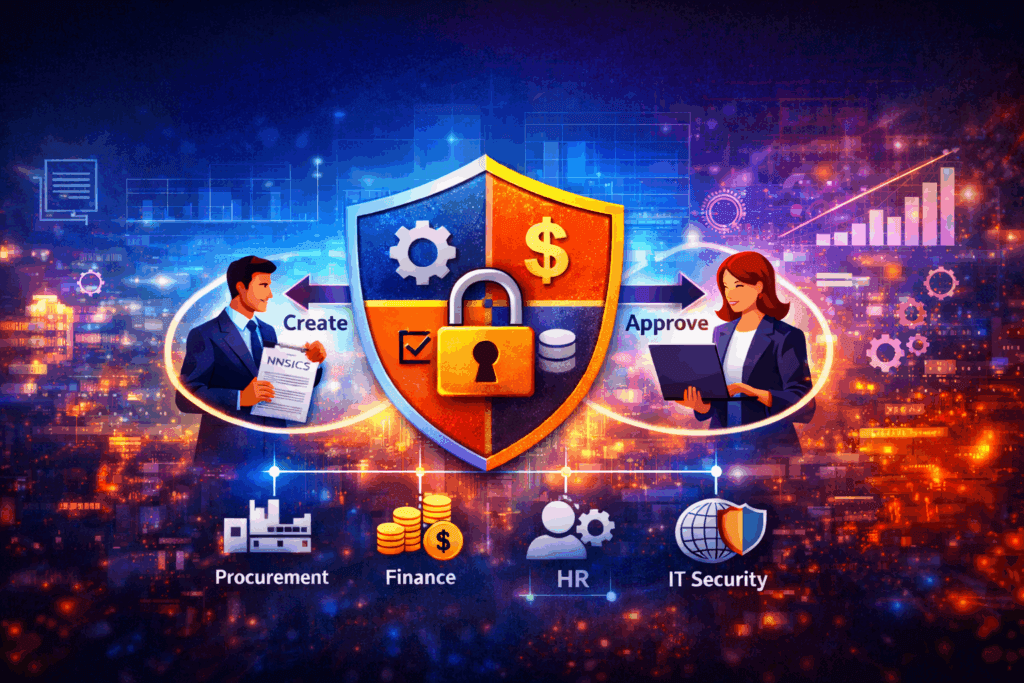
Segregation of Duties: The Most Critical and Complex Control in Modern ERP
In today’s digital-first enterprises, ERP systems sit at the core of business operations, supporting finance, procurement, HR, supply chain, and mission-critical decision-making. While these platforms enable scale and efficiency, they also introduce a significant risk when access is not governed correctly: conflicting or excessive user privileges. This is where Segregation of Duties (SoD) becomes not just important, but essential. Why…
How ERP Role-Based Access Control Aligns Functional Efficiency and Security?
As enterprises scale and digitize operations, ERP environments become increasingly complex, supporting multiple departments, geographies, partners, integrations, and automation. While this complexity enables growth, it also introduces significant access and security risk. The challenge for modern organizations is clear: how do you maintain operational efficiency without compromising security? The answer lies in a well-designed ERP role-based access control (RBAC) tool. Understanding…
Identity Governance for ERP Isn’t Complete Without Segregation of Duties
As enterprises continue to modernize their ERP environments, identity has become the new security perimeter. Users, roles, service accounts, bots, and third-party integrations now access critical ERP functions across finance, HR, procurement, and supply chain operations. While many organizations invest heavily in access controls and role management, identity governance for ERP remains incomplete without one foundational control: Segregation of Duties…