Segregation of Duties Analysis: Finding the Right Frequency
One of the most common questions organizations ask when implementing Segregation of Duties (SoD) controls is:
“What is the ideal frequency for conducting segregation of duties analysis?”
There is no single, definitive answer. The right frequency depends on each organization’s size, complexity, risk exposure, and rate of change.
Traditionally, SoD analysis was performed quarterly by external auditors or consultants. Organizations would receive reports, remediate identified issues, and aim to achieve compliance by the end of the fiscal year. However, this approach is no longer sufficient in today’s fast-paced, digital business environment.
With the emergence of next-generation SoD solutions, organizations now have full ownership of their data and controls, eliminating the dependency on third-party audits for ongoing analysis.
Why Periodic SoD Analysis Is No Longer Enough?
In modern enterprises:
- User populations change frequently
- Roles and responsibilities are continuously evolving
- Systems undergo regular updates, patches, and configuration changes
- Cyber and insider threats are increasing
Running SoD analysis once a year or even quarterly leaves organizations exposed to prolonged periods of risk. Quarterly reviews often fail to detect violations that arise from rapid organizational and system changes.
What Is the Right Frequency for SoD Analysis?
The frequency of SoD analysis should align with the pace of change within the organization, including both business and technology factors such as:
- User provisioning and deprovisioning
- Role changes and access modifications
- System upgrades and deployments
- Configuration and security updates
Recommended SoD Analysis Frequency by Organization Size
- Large, complex organizations – with frequent access and system changes, daily SoD analysis is recommended to ensure continuous risk visibility.
- Medium-sized organizations – with moderate changes, weekly SoD analysis provides a balance between control and operational efficiency.
- Smaller organizations – with limited system changes, quarterly SoD analysis may be sufficient, provided risks are closely monitored.
The key is to ensure that SoD analysis keeps pace with change, not lag behind it.
How to Be Proactive and Effectively Manage SoD Risks?
Proactive risk management requires moving from periodic checks to continuous monitoring and automation.
1Trooper’s SoD management tool enables organizations to:
- Proactively identify and manage access risks
- Segregate access across multiple accounts, applications, and systems
- Automate the entire SoD lifecycle, from detection to remediation
By analyzing each account’s access privileges, the platform:
- Identifies and reports financial and operational risks across roles
- Provides actionable remediation recommendations
- Anticipates risks from user activity and shifting responsibilities
- Automatically resolves conflicts wherever possible
Why Choose 1TRS for Continuous SoD Management?
At 1TRS – 1Trooper Risk Services, we help organizations transform SoD from a periodic compliance task into a continuous, intelligent risk management process.
Our solution ensures:
- Reduced fraud and error risk
- Continuous compliance and audit readiness
- Lower operational overhead
- Greater visibility into access-related risks
Ready to Optimize Your SoD Analysis Frequency?
Discover how 1Trooper’s automated SoD management solution can help you stay ahead of risks, no matter how fast your organization evolves.
- #1Trooper
- Segregation of Duties Analysis
- Segregation of Duties Controls
- SoD Analysis Frequency
- SoD Automation
- SoD risk management
Related articles
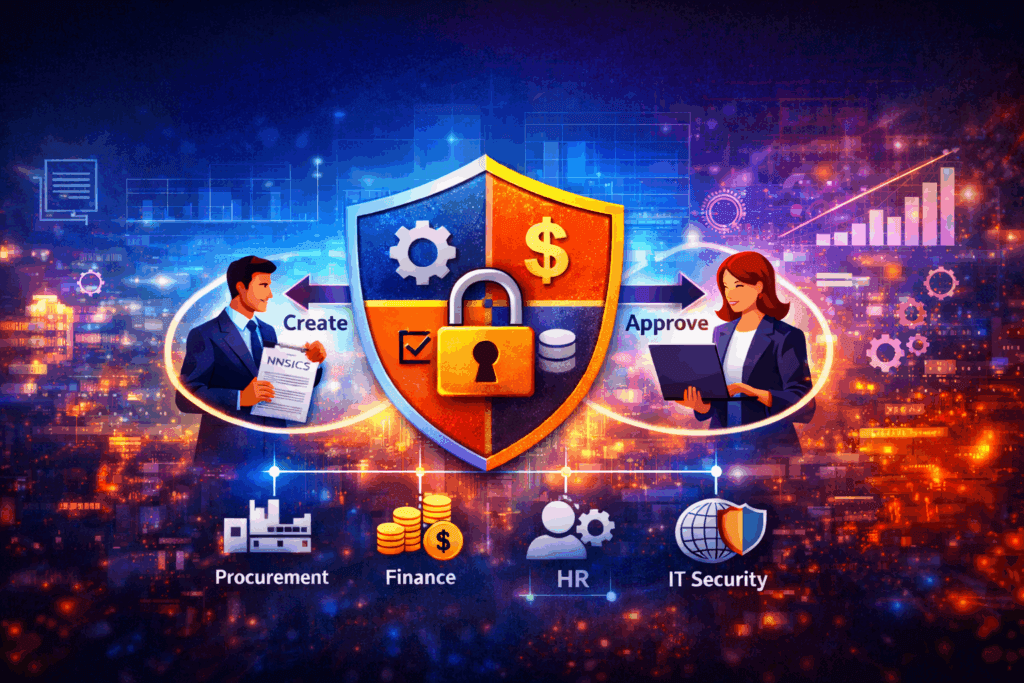
Segregation of Duties: The Most Critical and Complex Control in Modern ERP
In today’s digital-first enterprises, ERP systems sit at the core of business operations, supporting finance, procurement, HR, supply chain, and mission-critical decision-making. While these platforms enable scale and efficiency, they also introduce a significant risk when access is not governed correctly: conflicting or excessive user privileges. This is where Segregation of Duties (SoD) becomes not just important, but essential. Why…
How ERP Role-Based Access Control Aligns Functional Efficiency and Security?
As enterprises scale and digitize operations, ERP environments become increasingly complex, supporting multiple departments, geographies, partners, integrations, and automation. While this complexity enables growth, it also introduces significant access and security risk. The challenge for modern organizations is clear: how do you maintain operational efficiency without compromising security? The answer lies in a well-designed ERP role-based access control (RBAC) tool. Understanding…
Identity Governance for ERP Isn’t Complete Without Segregation of Duties
As enterprises continue to modernize their ERP environments, identity has become the new security perimeter. Users, roles, service accounts, bots, and third-party integrations now access critical ERP functions across finance, HR, procurement, and supply chain operations. While many organizations invest heavily in access controls and role management, identity governance for ERP remains incomplete without one foundational control: Segregation of Duties…